
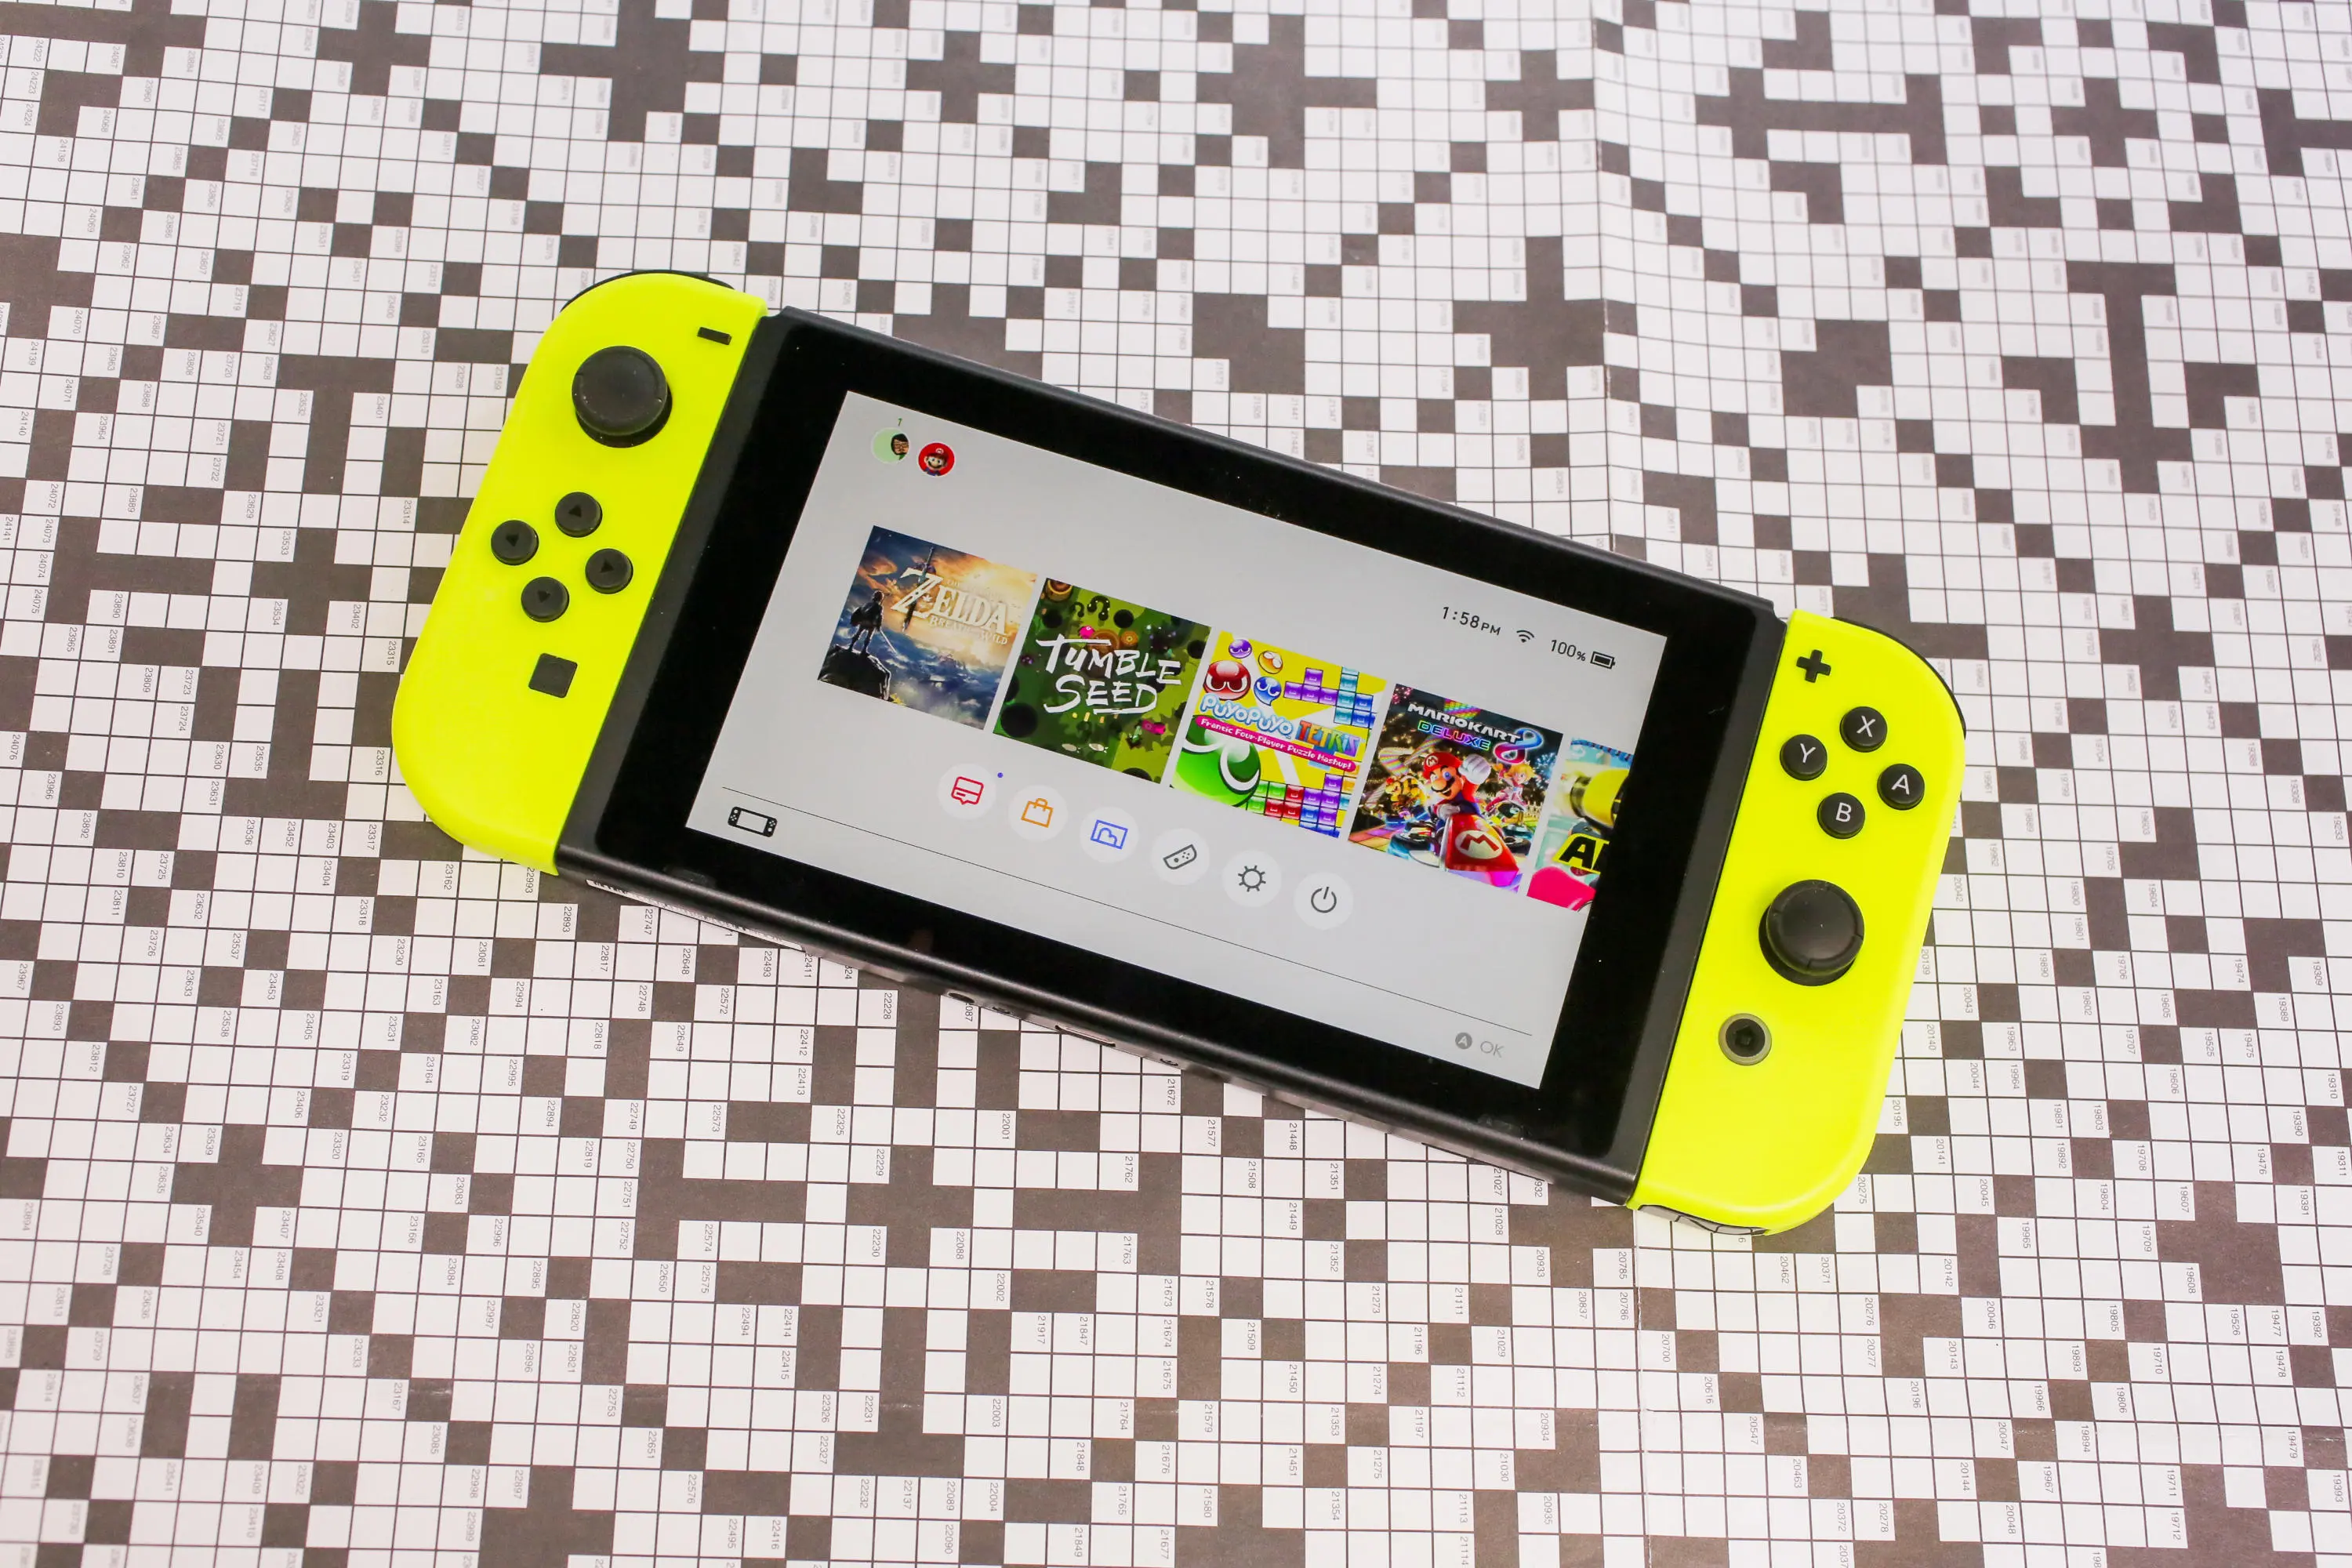
Original Nintendo Switch owners have a security exploit to address. 9 and disclosed a vulnerability (PDF) the following day, recommending that all original Switch users update immediately.
What happened
Nintendo released firmware version 23. 0. 0 on Sept. The Switch 2 isn’t affected by this particular issue, and Nintendo hasn’t shared specifics about what the exploit does. However, the company’s recommendation is clear, and the update that fixes these concerns is available now. Here’s how to check your firmware version and install the patch if you haven’t already.
Where the sources line up
The vulnerability applies only to original Nintendo Switch owners who use the Send to Smartphone feature. This feature generates a QR code on the Switch that users can scan with a smartphone, allowing them to transfer game captures and screenshots directly to their phone.
Practical impact for readers
Should someone else scan the QR code before you, they can connect their device to your Switch and use the connection to run unauthorized code on your Switch or steal information stored on the game console. Since your account information is stored on your Switch, that’s information you don’t want in the hands of someone else.
Who should pay attention now
The fix is simple. Nintendo released update 23. 0. 0 on Sept. 9, which fixes the exploit. It’s recorded as CVE-2026-82079, which is “a stock-based buffer overflow vulnerability” that lets attackers within wireless range execute code. It only affects the original Switch on firmware versions older than 23.
What is still unclear
To update your Nintendo Switch, head to System Settings > System > System Update to apply the update. Follow any additional on-screen prompts to install the update.
Latest comments
0No comments yet. You can start the conversation.